
Core Event: Reco Secures $55M, Valuation More Than Doubles
AI agent security startup Reco announced a $55 million funding round on September 29, 2026. Participants include AT&T Ventures, Forestay, and Quadrille Capital, building on its $30 million Series B in February. This extends the company’s total capital to $140 million.
Key hard facts:
- Funding round: Series B extension (same round extended)
- New funding amount: $55 million
- Total capital raised: $140 million
- Post Money Valuation: More than doubled since February, CEO estimates “high hundreds of millions”
- Annual Recurring Revenue (ARR): “Double-digit millions”, expected to triple in 2026
- Customer count: Over 100, with financial services representing ~40% of business
Market Reality: The Unmanaged “Agent Sprawl”

The term “AI sprawl” has transitioned from buzzword to operational challenge. Enterprises deploying AI agents at scale now face a new type of sprawl: a proliferation of vendors claiming to secure them.
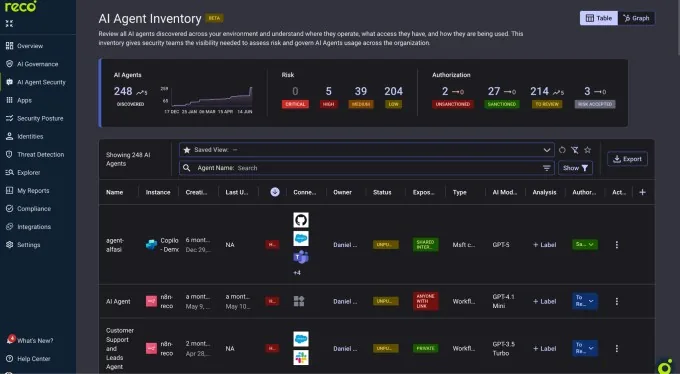
Reco pivoted from SaaS and AI platform mapping/monitoring to a broader solution using a context graph connecting agents to applications, people, accounts, and permissions. This enables security teams to visualize agent access and revoke unnecessary permissions.
The startup repeatedly discovers agents organizations were unaware existed: at a Fortune 100 customer, Reco found 21,000 unrecorded agents; at a financial services client, it identified an agent set up by a former employee capable of accessing Salesforce and exfiltrating data to an invisible domain.
These findings are not isolated. Cymphony reported ~85,000 files accessible to AI tools at one U.S. public company; HiddenLayer’s CEO noted over 50 customers have production AI agents touching critical systems.
Competitive Landscape: Multiple Approaches to Agent Security
Public data shows at least two dozen companies offering AI agent security solutions, broadly segmented by approach:
- Tool vetting: Assessing/authorizing external tools agents may use
- Data access control: Restricting what data agents can query or process
- Endpoint controls: CrowdStrike and others embedding detection and response capabilities on devices where agents run
- Unauthorized usage detection: Finding and remediating ad-hoc, unapproved deployments
Reco differentiates through existing integrations with 280+ applications (new integrations in days), plus browser and network signal triangulation to discover agents outside directly connected apps. Its platform inspects prompts and tool calls for security violations.
Getting Started: Who Should Adopt What
- Ready to adopt now: Mid-to-large enterprises with 10+ deployed agents and unclear governance; regulated industries (finance, healthcare) with fragmented access controls; organizations using multiple point tools without unified visibility
- Recommended to wait: Teams still in experimentation phase (fewer than 10 agents) with clearly bounded permissions; organizations using only SaaS-native agents without external tool integrations
Final Thought
Agent security has shifted from “if needed” to “how fast can we deploy.” When the pace of internal agent development outstrips governance capacity, the vendor sprawl itself becomes a new risk vector—the ultimate competition will be less about feature lists and more about integration depth and automated response within existing security operations.